> For the complete documentation index, see [llms.txt](https://propus.gitbook.io/hackbook/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://propus.gitbook.io/hackbook/writeups/dockerlabs/vulnvault.md).

# 🟩 Vulnvault

🧠Dificultad: Fácil | 🔓16/10/2025

## 🕵️ Reconocimiento

Comenzamos con un escaneo de puertos con `nmap`:

```bash
nmap -sC -sV -Pn $IPTARGET | tee nmap
```

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2F8PncuRwy6YchYrkEcTC3%2FPasted%20image%2020251015190452.png?alt=media&amp;token=d0f54905-e5c8-4c78-8cab-14d276823c53" alt=""><figcaption></figcaption></figure>

Como hay un servicio `HTTP` activo, hacemos un escaneo de directorios:

```bash
ffuf -w /usr/share/wordlists/SecLists-2025.2/Discovery/Web-Content/directory-list-lowercase-2.3-medium.txt:FUZZ -u http://$IPTARGET/FUZZ -e .html,.php,.txt,.xml,.js
```

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FbczhbHIGzss6ilKS0okp%2FPasted%20image%2020251015192905.png?alt=media&amp;token=d49bfe57-ed34-4f20-bb23-f33773f8c183" alt=""><figcaption></figcaption></figure>

En el directorio `/index.php` hay un apartado llamado `Acerca de` donde nos da a entender que la función de generar reportes puede ser vulnerable a `Command Injection`:&#x20;

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FQVal3BLodwyJUGkzxmAs%2FPasted%20image%2020251015190557.png?alt=media&amp;token=f6c07889-9dc6-4a2b-ae6f-53bcd26dc331" alt=""><figcaption></figcaption></figure>

El apartado para generar nuestros reportes es el siguiente:

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FbvI90WsN7MeBJabqa9eQ%2FPasted%20image%2020251015190858.png?alt=media&amp;token=196ebe2f-afa0-4235-a13c-6d4051b244b3" alt=""><figcaption></figcaption></figure>

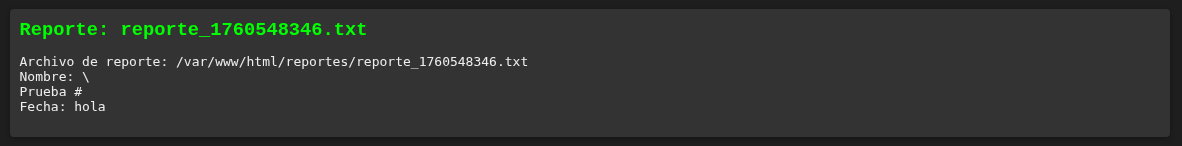
Si probamos a introducir en algún campo la siguiente cadena:

```plaintext
; echo "Prueba"
```

Vemos que se ha ejecutado el comando.

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FOokJbWwISzqvdNyUv0K7%2FPasted%20image%2020251015191300.png?alt=media&amp;token=1cb9ed7e-961d-4f81-816c-52b557a25c13" alt=""><figcaption></figcaption></figure>

## 🚪 Ganando acceso

Vamos a intentar inyectar una reverse shell. Para ello, vamos a ver algunos binarios que hay disponibles en el sistema con el comando `which`:

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FqQW2wrgXnikwl5v0T0vb%2FPasted%20image%2020251015191637.png?alt=media&amp;token=f460b47a-c937-454f-944c-9830b15963dc" alt=""><figcaption></figcaption></figure>

Tenemos `python3`, `bash` y `sh`. Aunque no aparezca en la captura, también tenemos `php` y otros binarios que nos pueden servir.

Probamos a mandar la reverse shell:

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FgDFFZmWvAxxqDUxNBFmX%2FPasted%20image%2020251015191713.png?alt=media&amp;token=810405e6-886e-4193-94e8-47ea9eebbedc" alt=""><figcaption></figcaption></figure>

Pero a nuestra máquina no nos llega ninguna petición. Intentando con distintas reverse shells, vemos que no funciona correctamente. Es posible que el código `php` esté escapando algunos caracteres.

Vamos a intentar ver qué usuarios hay en el sistema:

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FqBj144YmlE937DuCPNEF%2FPasted%20image%2020251016164232.png?alt=media&amp;token=50e1d22e-12f6-434e-affb-e591ba0861c5" alt=""><figcaption></figcaption></figure>

Existe un usuario llamado `samara`. Curiosamente tenemos permisos para ver su `/home`:

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FIhzb7G28OJwwPeqdQRwp%2FPasted%20image%2020251016164328.png?alt=media&amp;token=c80b5261-575c-4cd6-9a35-711792aa81e7" alt=""><figcaption></figcaption></figure>

Podemos obtener el `id_rsa` de `samara` para acceder por `ssh`:&#x20;

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2Fg6GMZ1DpPVOejVTuS9DU%2FPasted%20image%2020251016164421.png?alt=media&amp;token=613668e6-e57d-4870-896c-0263b1182045" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FjUlThQ2tyvEIBY3YcBFm%2FPasted%20image%2020251016164617.png?alt=media&amp;token=9093d17b-53f5-47d1-88c6-9942edc77141" alt=""><figcaption></figcaption></figure>

Lo copiamos a nuestra máquina y le damos permisos de lectura/escritura:

```bash
chmod 600 id_rsa
```

Ahora si podemos acceder por `ssh` con el `id_rsa`:

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FXfv0rljwXvg6V9iYvgLq%2FPasted%20image%2020251016164554.png?alt=media&amp;token=873820bf-0e2d-47f9-93b5-a333878bdc45" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FkLdqBsnV8GaIQ0yrivo7%2FPasted%20image%2020251016164759.png?alt=media&amp;token=6a46341b-33e8-4cd1-a181-beab94a02a4a" alt=""><figcaption></figcaption></figure>

## 💥 Escalada de privilegios

Una vez dentro de la máquina, listamos los servicios que están corriendo.

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2Fqbt19WuUcptF0LudevyL%2FPasted%20image%2020251016164941.png?alt=media&amp;token=fce0a954-aa31-4e9f-ab24-1a809cfdbed8" alt=""><figcaption></figcaption></figure>

Nos fijamos que se está ejecutando el script localizado en `/usr/local/bin/echo.sh` como `root`. Para este script, tenemos permisos de escritura, por lo que podemos modificarlo.

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FiRLg4AH09qngMA9RAYZI%2FPasted%20image%2020251016164927.png?alt=media&amp;token=e8727ed2-fbe9-41e2-9fa0-3128cdd567ed" alt=""><figcaption></figcaption></figure>

En mi caso, voy a hacer que el binario `/bin/bash` tenga el bit `SUID` activado para obtener una shell con `root` fácil.

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FhGG3QBZHS9ESeq6zLkz1%2FPasted%20image%2020251016165200.png?alt=media&amp;token=2215aa24-c035-401c-8b8b-842d16c31d74" alt=""><figcaption></figcaption></figure>

Si esperamos, vemos que ahora el binario efectivamente tiene el bit `SUID` activado. Ejecutamos `/bin/bash -p` para lanzar una shell con permisos del propietario (`root`):

<figure><img src="https://3832202623-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FhaHYQaFsZAHOyVtSUS1x%2Fuploads%2FfbQFzXhLStPnvemjwLWP%2FPasted%20image%2020251016165256.png?alt=media&amp;token=7e500504-99b2-4968-b91d-c4ff23f2efff" alt=""><figcaption></figcaption></figure>